 websec
What was reported
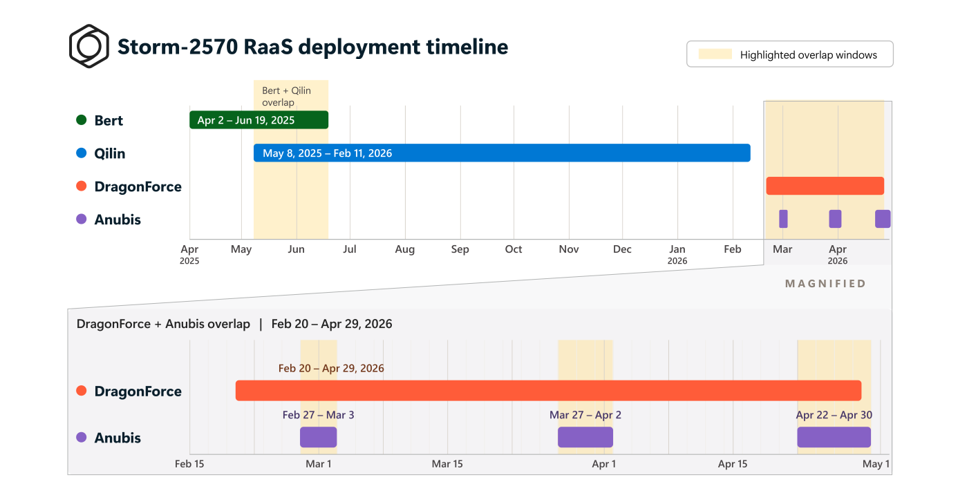
Microsoft describes consistent post-compromise behavior associated with Storm-2570 across incidents involving Qilin, DragonForce, Anubis and BERT ransomware. Its investigation emphasizes recurring remote access, credential access, security tampering and data movement. The initial access method remains unconfirmed in the published account.
Why it matters
The name of the final ransomware family is only one part of an incident. Earlier records can reveal activity before encryption and help responders determine the scope of compromise. Similar tools alone do not establish attribution: legitimate administration can leave overlapping traces.
Forensic focus
Preserve endpoint and identity records, remote-support installation history, relevant network logs and backup events. Build a timeline that separates direct observations from interpretations. Validate unfamiliar administration against change records and known operator activity. Treat a vendor's actor assessment as attributed research, not an independent finding about your own systems.
Source published 24 September 2026. Briefing prepared 26 September 2026.